
MPLS/VPN with SR-MPLS Core
As we discussed in the BGP-Free Core with SR-MPLS blog post, SR-MPLS works as a drop-in replacement for the traditional MPLS control plane. No wonder it works well (when properly implemented) with MPLS/VPN services – the second “fun” scenario in my ITNOG10 Segment Routing workshop. It uses the same topology as the BGP-Free Core scenario:
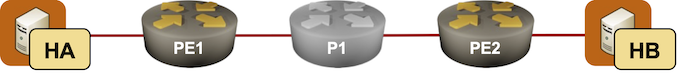
Simplest possible MPLS/VPN network with SR-MPLS core
Does It Work?
Of course. After the BGP session is established between the PE routers (which implies IS-IS is working), the VRF routes get the familiar two-label stack:
pe1#show ip route vrf tenant 172.16.1.0/24 | begin 172.16B I 172.16.1.0/24 [200/0]via 10.0.0.3/32, IS-IS SR tunnel index 2, label 116384via 10.1.0.1, Ethernet1, label 900003
Lab Topology
Here are the changes I made to the lab topology to enable MPLS/VPN services:
- I had to enable MPLS/VPN and disable LDP:
mpls.vpn: Truempls.ldp: False
- The edge devices (PE routers) use a different set of modules: IS-IS, SR-MPLS, BGP, MPLS (which includes MPLS/VPN) and VRF:
groups:edge:members: [ pe1, pe2 ]module: [ isis, bgp, sr, mpls, vrf ]
- Finally, the PE-to-host links are moved to the tenant VRF:
vrfs:tenant:links: [ ha-pe1, hb-pe2 ]
Try It Out
The workshop GitHub repository includes the installation guidelines; you might want to read them first. After that, you can:
- Start a GitHub Codespace
- Import an Arista cEOS container into it (alternate step-by-step instructions)
- Change directory to
2-fun/2-mpls-vpn - Execute netlab up
- Have fun