
Sunsetting netlab Vagrant/libvirt provider
When I started the netlab project, Vagrant was the go-to tool if you wanted to build a virtual environment described in a text configuration file (an idea popularized as infrastructure-as-code). It wasn’t ideal for what we were doing, but a tool rarely does a great job when used far away from its intended use case.
netlab initially supported Vagrant with VirtualBox, quickly adding support for KVM/libvirt through the vagrant-libvirt plugin. Life was good… until it wasn’t.
How vagrant-libvirt Plugin Deals with Duplicate Subnets
TL&DR: Badly. The vagrant-libvirt plugin mysteriously crashes when an existing virtual network (with a different libvirt name) uses the same IP subnet as the desired management network.
Background: netlab is using the vagrant-libvirt plugin to manage libvirt/KVM virtual machines with Vagrant. As I already have that infrastructure, I use it to start standalone virtual machines (usually to test various Ubuntu releases) on my Linux server. Things work great… until they don’t.
Here’s how I managed to waste half a day chasing imaginary gremlins caused by a simple error.
MPLS/VPN with SR-MPLS Core
As we discussed in the BGP-Free Core with SR-MPLS blog post, SR-MPLS works as a drop-in replacement for the traditional MPLS control plane. No wonder it works well (when properly implemented) with MPLS/VPN services – the second “fun” scenario in my ITNOG10 Segment Routing workshop. It uses the same topology as the BGP-Free Core scenario:
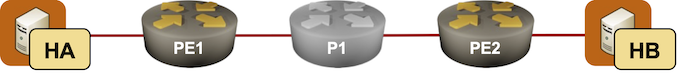
Simplest possible MPLS/VPN network with SR-MPLS core
Configuring Management IP Addresses to Virtual Network Devices
It goes without saying that if you want to configure (virtual) network devices with any semi-sane configuration mechanism1, the device must have a working IP address. Here’s the time-honored method2 to assign an IP address to a virtual network device:
- Start the virtual machine (using a GUI)3
- Open a new window: either a telnet session to the virtual console port or a full-blown virtual console (GUI) session.
- Manually configure the IP address, the SSH server, and the user credentials on the first interface.
Worth Reading: NatJack
Repeat after me: NAT is not a security feature
Every time I wrote something along the lines of NAT is not a security feature, I got the expected pushback from people defending their bad suboptimal design choices.
Fortunately, rational1 engineers no longer need to have that discussion: the NatJack website documents2 a half-dozen attacks on typical NAT implementations.
Obvious next step: coping mechanisms like “this is all theoretical”, like the “but the remote host cannot reply” argument made 23 years after the Slammer worm 🤦♂️.
Worth Reading: An Interactive Introduction to the STP
I can’t even start imagining how much time Vincent Bernat spent creating his interactive introduction to the spanning tree protocol (starting with STP implemented in WebAssembly); the results are simply phenomenal (there’s also a video version for people who forgot how to read).
I don’t think we’ll ever need another STP intro after this one ;)
Please Help Me Follow Your Content
Finding good content in the swamp of AI slop is hard, and whenever I find a blog post worth reading, I’d like to know when the author publishes the next one.
For stupid reasons (like a day having only 24 hours, and me having a life), I can’t periodically scan all websites I find interesting, but fortunately, I don’t have to. Two well-known mechanisms work reliably: email updates and RSS feeds.
BGP-Free Core with SR-MPLS
The beauty of SR-MPLS is that it’s a drop-in replacement for the traditional (LDP- or RSVP-based) MPLS control plane. For example, you could replace LDP with SR-MPLS in a network using MPLS to implement a BGP-free transport core, and it just keeps working.
This scenario was the first “fun” scenario in the ITNOG10 Segment Routing workshop. The core network uses the same topology as in the previous examples; I added two hosts and BGP routing.
Simplest possible network using a BGP-free core
Networking Aspects of Running VMs in Containers
It's spaghetti all the way down (see also RFC 1925 rule 6a)
The vrnetlab project and its containerlab fork implement a wonderful idea: let’s package virtual machines (primarily network devices that cannot be containerized) as containers to use reliable orchestration tools like containerlab to provision network topologies.
That approach might have a few drawbacks (depending on how the container images are built), but the obvious elephant in the room is: how do you make the virtual network plumbing work?
MUST READ: Git – Going Pro
I sure wish Tony Mattke had started publishing his Git-related blog posts in 2017 when I was still struggling with the basics. In his latest Going Pro article he covers:
- Using SSH keys with Git and GitHub
- Pre-commit hooks
- GitHub Actions and linting
- GitHub Branch protection
- PR reviews
- gh CLI
Absolutely worth every second you’ll spend reading the article!